Audit · Secure · Ship fearlessly
Find security issues in your vibe-coded apps before they ship.
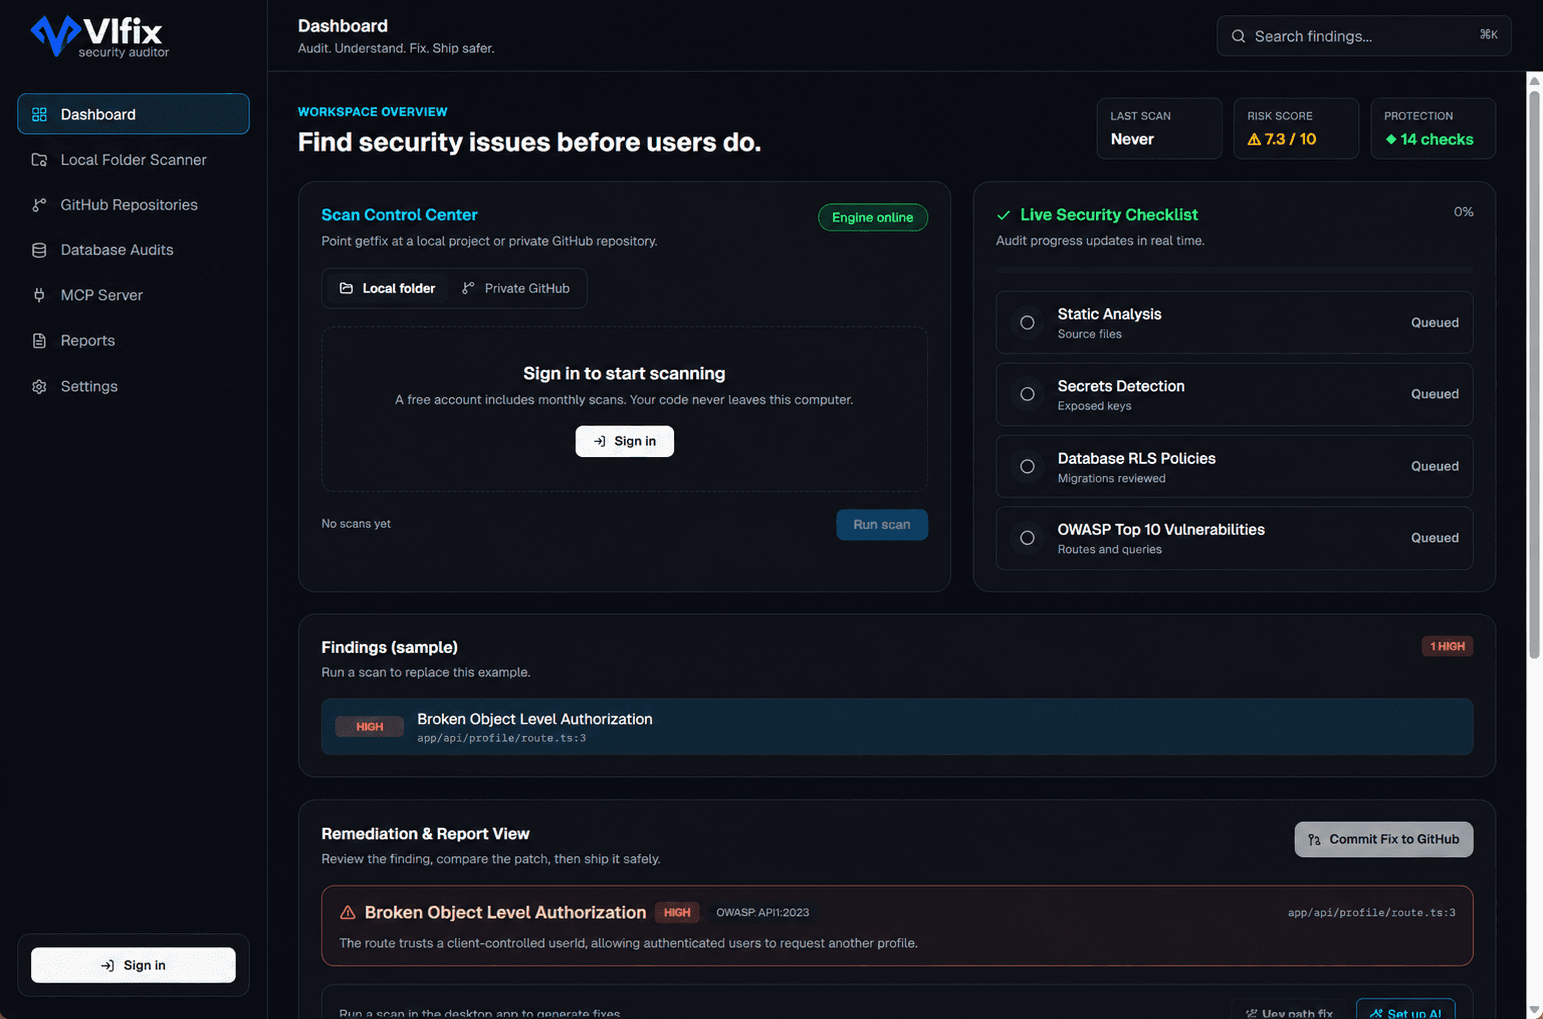
VIfix scans your code, configs, API routes and Supabase policies for real-world security risks, explains them in plain English, and gives you production-ready fixes, so you can ship faster and safer.
- No credit card required
- Scan in minutes
- Your code stays on your machine
Built for the stacks you ship with
- Next.js
- React
- Supabase
- Stripe
- Node.js
- TypeScript
- Prisma
- Python
How it works
From code to confidence in four simple steps
Go from unscanned to ship-ready in minutes.
- 1
Connect your repo
Link a GitHub repo or scan a local folder.
- 2
Run automated audit
We check your code, configs, API routes and database policies.
- 3
Review findings
Get clear explanations and code diffs.
- 4
Commit safer fixes
Apply fixes locally or open a PR with confidence.
Detailed reports
Clear findings. Real fixes.
Go beyond vague alerts. VIfix gives you detailed reports, code diffs and step-by-step remediation guides so you can fix issues with confidence.
- Plain-English explanations
- Code diffs and fix suggestions
- OWASP Top 10 coverage
- Supabase RLS and database checks
- Learn as you fix with educational content
Pricing
Simple, transparent pricing
Start for free and upgrade as you grow. No hidden fees.
Free
$0/forever
For hobby projects and trying VIfix out.
- 10 scans / month
- 5 AI fixes / month
- Secrets, OWASP & Supabase RLS checks
- Local folders + private GitHub repos
- Apply fixes locally
- Community support
Pro
Most popular$19/month
For indie hackers shipping to production.
- 500 scans / month
- 300 AI fixes / month
- Secrets, OWASP & Supabase RLS checks
- Local folders + private GitHub repos
- One-click fix pull requests
- Email support
Max
$49/month
For power users and agencies scanning many apps.
- Everything in Pro
- Unlimited scans
- 1,500 AI fixes / month
- Priority support
- Secure payments via Stripe
- Cancel anytime
- Your code never leaves your computer
FAQ
Common questions
Everything you need to know about VIfix.
Does VIfix access my private code?
Scans run on your computer. Private GitHub repos are downloaded to a temporary folder on your machine using your own token, scanned, then deleted. Your code is never uploaded to VIfix's servers.
Can it scan local folders?
Yes. Point VIfix at any project folder. It skips node_modules, build output and files in your .gitignore, and never follows symlinks outside the project.
Does it fix issues automatically?
It proposes fixes; you decide. Every patch is shown as a diff, re-scanned to confirm the issue is gone, and only applied or opened as a pull request when you click. It never pushes to your main branch.
What stacks are supported?
JavaScript and TypeScript (Next.js, React, Node.js), Supabase and Postgres migrations, Prisma, Drizzle and Knex queries, plus secret detection across config files, shell scripts and Python.
What gets sent to the AI provider?
Only when you click “Generate AI fix”: the single affected file, with every detected secret replaced by a placeholder. You use your own Anthropic or OpenAI key.
Can I cancel anytime?
Yes. Manage or cancel your subscription from the app (Settings → Plan & billing). You keep Pro until the end of the billing period.
Ship safer, faster
Start scanning your app today
Find what your AI pair-programmer missed, before your users do.
No credit card required · Setup in minutes